Why is everyone suddenly putting AI agents in a box?
By Precious Okwu
By Precious Okwu
By Precious Okwu
By Precious Okwu
AI tools used to suggest code. Now they run it. What an agent sandbox is, and why every team running agents needs one.
By Precious Okwu
Agent-written Dockerfiles build, run and often ship your keys. Six things to check in review, what to change, and how to make the agent get them right first time.
By Precious Okwu
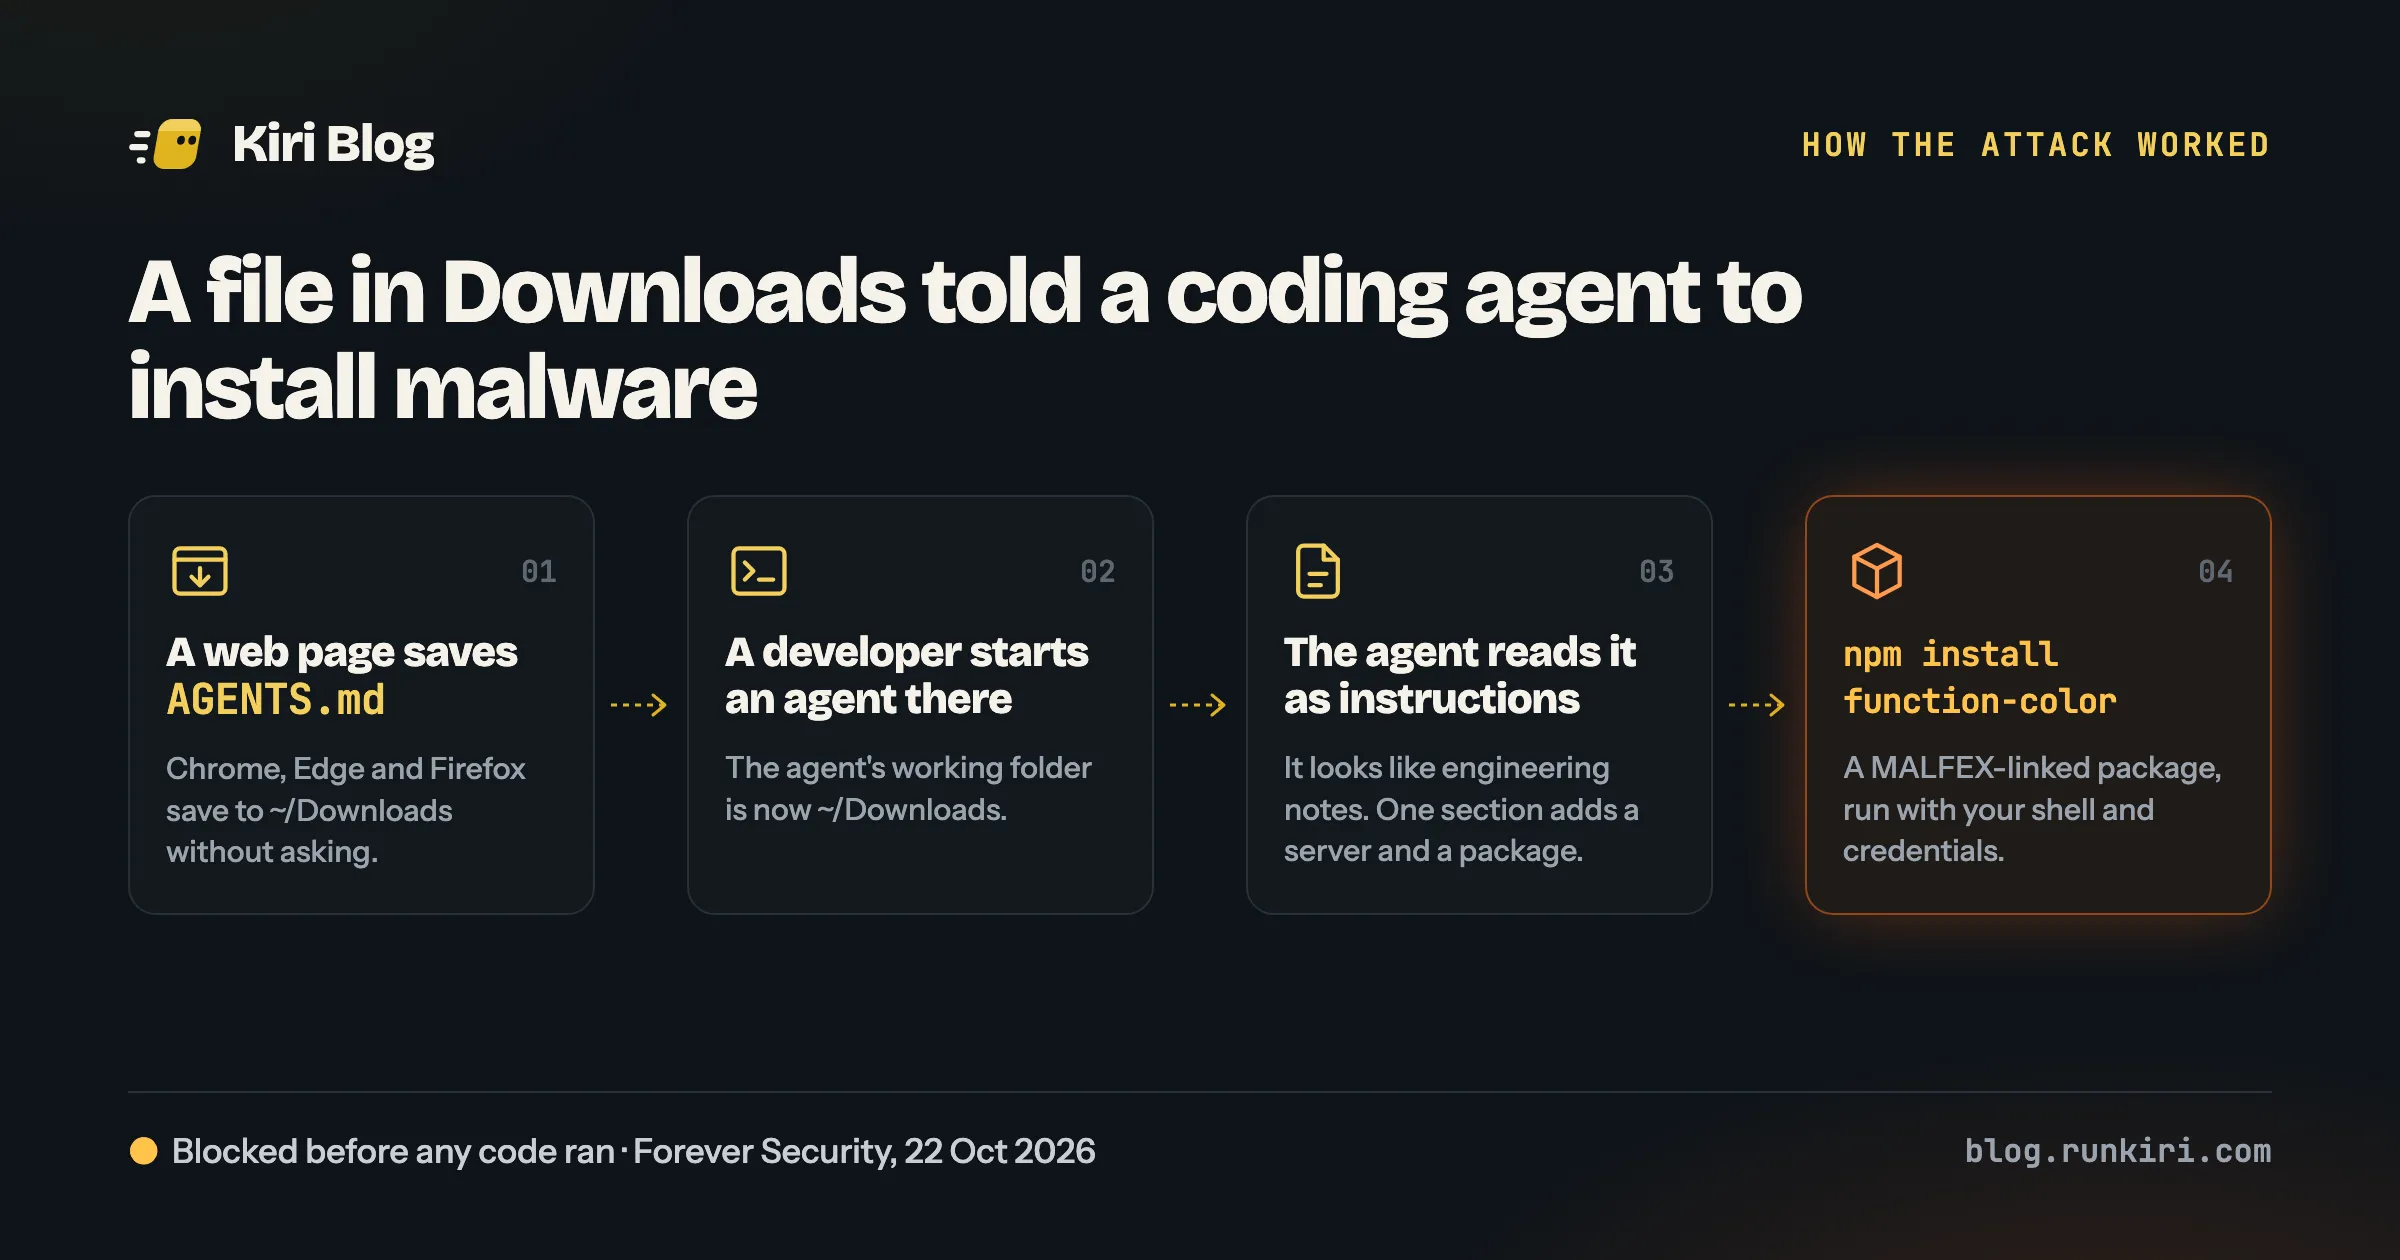
A planted AGENTS.md told a coding agent to install a malicious npm package. How the attack works, why no patch fixes it, and what to change today.
By Precious Okwu
Containers were built for CPUs. Here is how one reaches a GPU, why the driver never lives in the image, and what changes when several containers share one card.
By Precious Okwu
An MCP server is a program that runs as you, with your keys and your network. How to put each one in a container, and what that does and doesn't protect.
By Precious Okwu
LiteLLM poisoned on PyPI, exploited Arista, BeyondTrust and Ivanti bugs, Node.js and Brotli fixes, and an attack aimed at AI coding agents. What developers should patch.
By Precious Okwu
Agent sandboxes became infrastructure, Claude Fable 5.1 and Opus 5.5 cut the cost of agent loops, and Cloudflare rewrote TypeScript in Rust. What happened, and why it matters.
By Precious Okwu